
Gateway of Last Resort: A Beginner's Guide
The gateway of last resort is a router's fallback forwarding address for network traffic destined to unknown destinations. This post explains how it relates to the default route, how to configure it on a Cisco router, and how to interpret it in the routing table output. It's an essential concept fo
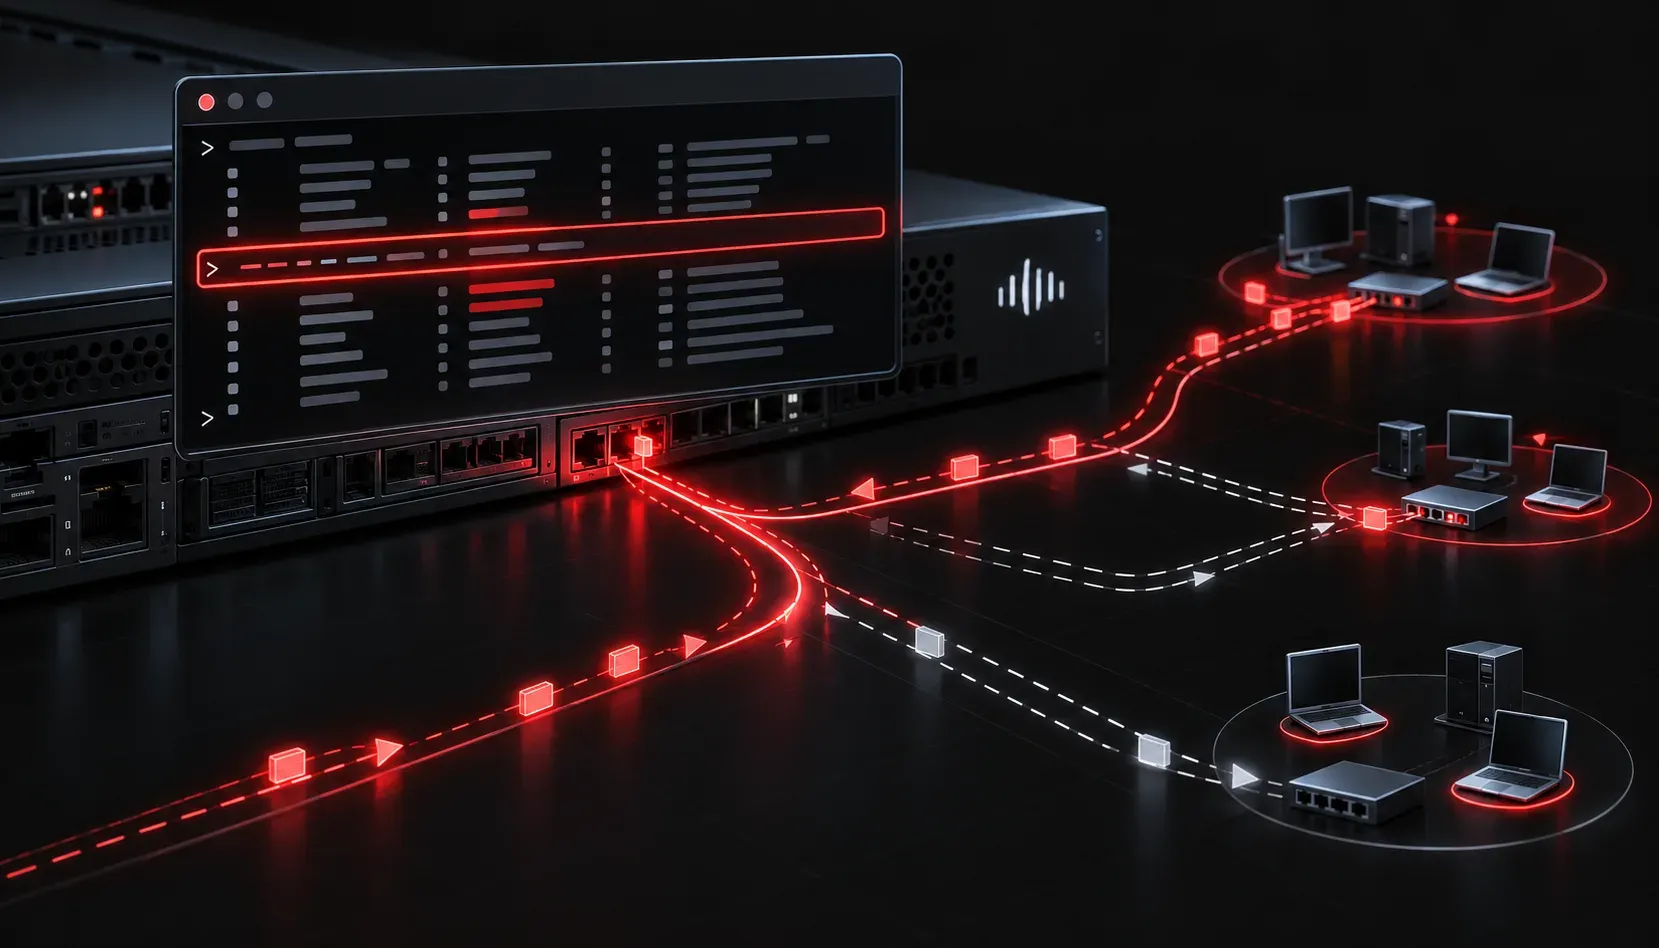
When a router receives a packet, it checks its routing table to figure out where to send it. But what happens when the destination address doesn't match any known route? That's where the gateway of last resort comes in.
Think of it like a post office that can't figure out which local carrier should handle a letter. Rather than throwing it away, they forward it to a regional hub that has a better chance of getting it to the right place. The gateway of last resort plays exactly that role in your network.
What Is the Gateway of Last Resort?
The gateway of last resort is the next-hop address a router will use when it has no more specific route for a destination. It's essentially the router's fallback plan for handling unknown destinations. Without it, a router would simply drop packets it doesn't recognize, which in most networks is not acceptable behavior.
The gateway of last resort is set by configuring a default route on the router. The two terms are closely related but technically distinct: the default route is the routing table entry, and the gateway of last resort is what the router displays as the forwarding address derived from that entry.
The Default Route Explained
A default route is written as 0.0.0.0/0 in IP routing. The notation means "match any destination address." Because it has the shortest prefix length possible (zero bits), it will always lose a match against any more specific route. This is intentional. It only takes effect when nothing else fits.
You can add a static default route on a Cisco router with this command:
Router(config)# ip route 0.0.0.0 0.0.0.0 192.168.1.1In this example, 192.168.1.1 is the next-hop address, typically the address of an upstream router or your ISP's gateway. Once this route is in place, the router will display the gateway of last resort in the routing table output.
Reading the Routing Table
After configuring the default route, you can verify it by running show ip route on the router. Here's what you'd expect to see at the top of the output:
Gateway of last resort is 192.168.1.1 to network 0.0.0.0

S*    0.0.0.0/0 [1/0] via 192.168.1.1
Let's break down what you're looking at:
- Gateway of last resort is 192.168.1.1: The router will forward unknown traffic to this address.
- S*: The
Smeans this is a static route. The asterisk (*) marks it as a candidate default route. - 0.0.0.0/0: This is the default route entry, matching all destinations.
- [1/0]: The administrative distance is 1, and the metric is 0.
- via 192.168.1.1: Traffic will be forwarded to this next-hop address.
If no default route has been configured, the routing table will instead show:
Gateway of last resort is not setSeeing this message is a red flag in most production environments. It means any packet destined for an unknown network will be silently dropped.
Why This Matters in Real Networks
In a typical enterprise setup, internal routers know about all the subnets inside the organization. But internet-bound traffic is destined for millions of addresses that no internal router tracks. Instead of loading every router with the entire internet routing table, you configure a default route pointing toward the firewall or edge router, which handles internet connectivity.
This keeps routing tables lean and makes network traffic flow predictably. Branch office routers, for example, almost always rely on a gateway of last resort to reach anything outside their local network.
What's Next
Now that you understand how routers handle traffic that doesn't match a specific route, the next logical step is exploring how routers learn routes dynamically. In the next post, we'll cover how routing protocols like OSPF work and how they advertise routes between routers automatically. Understanding the gateway of last resort makes those concepts much easier to follow.
Tools and resources for this topic
- Wendell Odom CCNA Vol 1 — Covers networking fundamentals, switching, and routing basics.
- Wendell Odom CCNA Vol 2 — Covers advanced routing, WAN, infrastructure services, and security.