
What is Third-Party Risk Assessment?
Third-party risk assessment is the process of evaluating the security posture of external vendors before and after engaging in business relationships. This post explains why vendor risk matters, what a thorough assessment covers, and how organizations tier vendors by risk level. It references the S

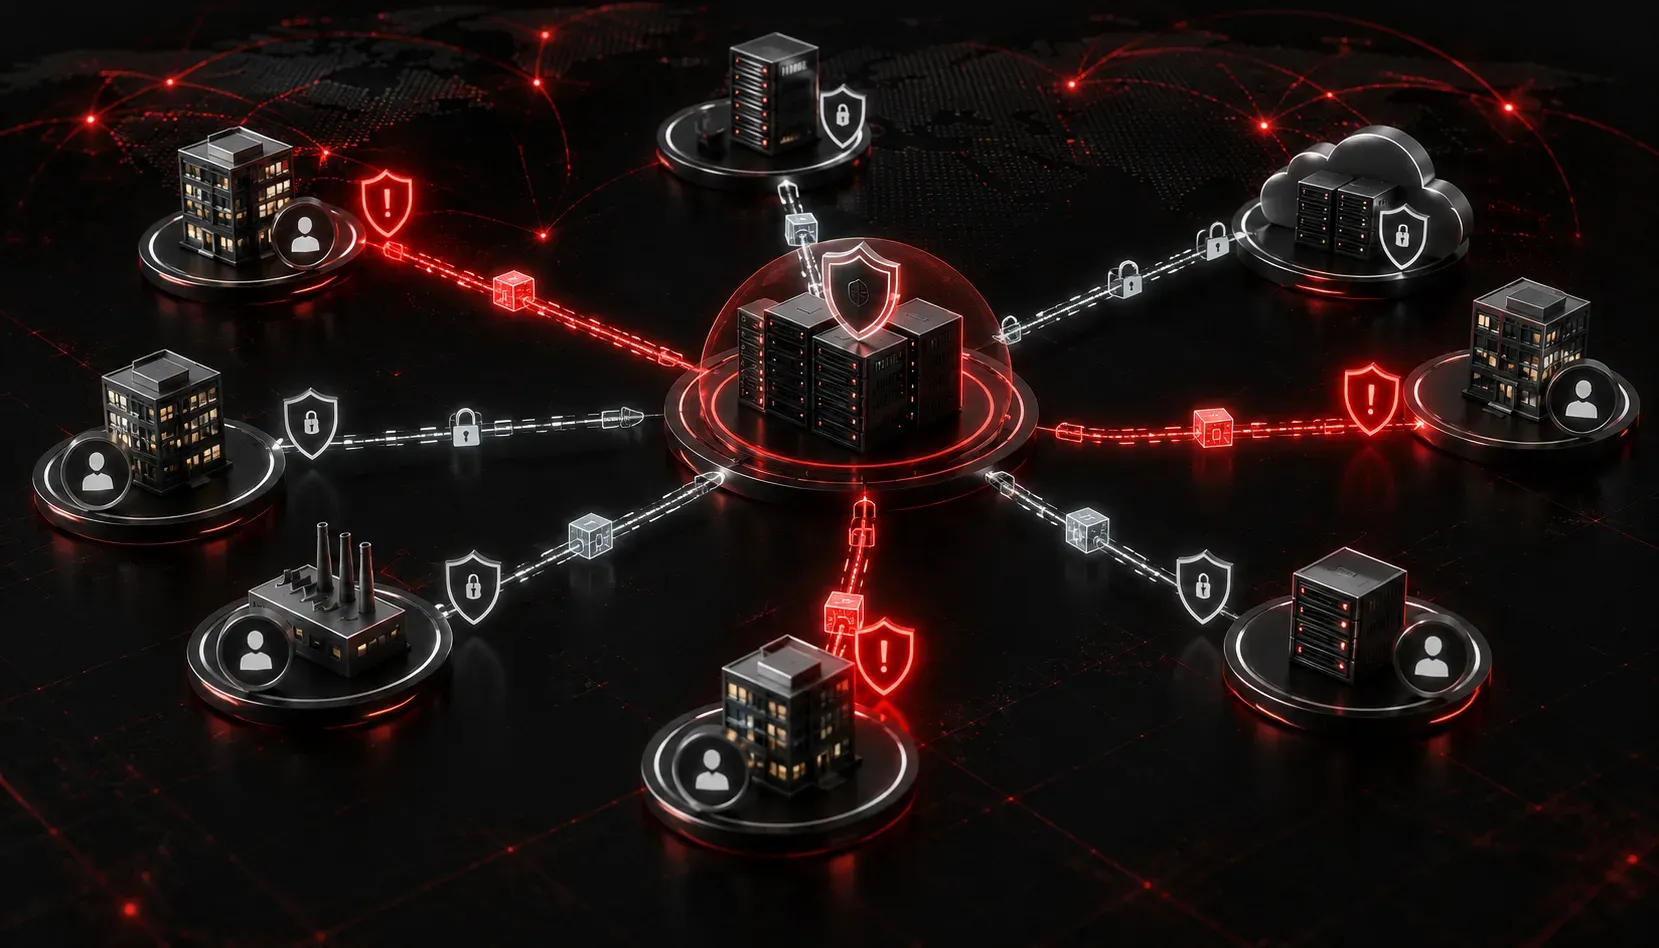
When you think about securing an organization, it's tempting to focus only on what's happening inside the network. But here's the reality: some of the most significant security threats don't come from hackers breaking through your firewall. They come through the front door, in the form of vendors, suppliers, and partners you've chosen to trust.
Third-party risk assessment is the process of evaluating the security posture of external organizations before and after you do business with them. If a vendor has access to your systems, your data, or your network, their security problems become your security problems. Understanding this concept is essential for the Security+ exam and for any real-world security role.
Why Third-Party Risk Matters
Think about a typical organization. They might use a cloud storage provider, a payroll processor, an IT support firm, and a dozen software-as-a-service platforms. Each of those relationships introduces vendor risk. If any one of those external vendors experiences a breach, is compromised by malware, or mishandles your data, your organization suffers the consequences.
The 2013 Target data breach is a textbook example of this concept. Attackers gained access to Target's point-of-sale systems through credentials stolen from an HVAC contractor. The contractor had legitimate access to Target's network, and that trust was exploited. The breach exposed 40 million credit card numbers and cost the company hundreds of millions of dollars.
This is exactly why third-party risk assessment exists. You cannot simply trust that your vendors are secure. You have to verify it.
What Does a Third-Party Risk Assessment Actually Look At?
A solid vendor risk review covers several key areas:
- Data handling practices: How does the vendor store, process, and transmit your data? Do they encrypt data at rest and in transit?
- Access controls: Who at the vendor has access to your systems or data? Is that access appropriately limited using the principle of least privilege?
- Compliance and certifications: Does the vendor hold relevant certifications like
SOC 2,ISO 27001, orPCI DSS? These demonstrate a baseline commitment to security. - Incident response capability: Does the vendor have a documented process for detecting and reporting a breach? Will they notify you in a timely manner?
- Business continuity: What happens to your data and operations if the vendor goes out of business or experiences a major outage?
- Subcontractors (fourth-party risk): Does your vendor use other vendors? Those relationships extend your risk surface even further.
How Organizations Conduct the Assessment
There are several practical tools organizations use when assessing external vendors:
- Questionnaires and surveys: Standardized security questionnaires, like those from the Shared Assessments Program, ask vendors to self-report their security practices.
- Contract review: Legal agreements should include security requirements, breach notification timelines, and the right to audit. This is sometimes referred to as a
right-to-auditclause. - On-site audits: For high-risk vendors, organizations may send their own security team to inspect controls in person.
- Continuous monitoring: Assessment isn't a one-time event. Tools can monitor a vendor's external attack surface on an ongoing basis, watching for signs of compromise or configuration drift.
Vendor Tiering: Not All Risk is Equal
Organizations typically categorize vendors by the level of access and sensitivity involved. A vendor with read-only access to anonymized marketing data is not the same risk level as a vendor who processes payroll or maintains admin credentials to your infrastructure. Tiering vendors lets security teams prioritize where they spend their assessment effort.
For example:
- Tier 1 (critical): Full audit, contract review, and ongoing monitoring required.
- Tier 2 (moderate): Security questionnaire and annual review.
- Tier 3 (low risk): Basic contractual terms and occasional check-ins.
What's Next
Now that you understand the foundation of third-party risk assessment, the next step is exploring specific vendor agreements and formal documents that define security expectations, including things like Memorandums of Understanding (MOUs), Service Level Agreements (SLAs), and Business Associate Agreements (BAAs). These legal frameworks are how organizations put third-party risk controls into writing, and they show up regularly on the Security+ exam.
If you want to go deeper on this and every other domain in the exam, pick up the CompTIA Security+ Study Guide by Mike Chapple and David Seidl. It's the most thorough resource available for building a solid foundation alongside your study here.