
How Vulnerability Management Works: A Simple Guide
This post explains the vulnerability management process in a clear, beginner-friendly way. It covers the five core phases of the vulnerability lifecycle: discovery, prioritization, remediation, verification, and reporting. The content maps directly to CCST Cybersecurity exam domain 4.1.

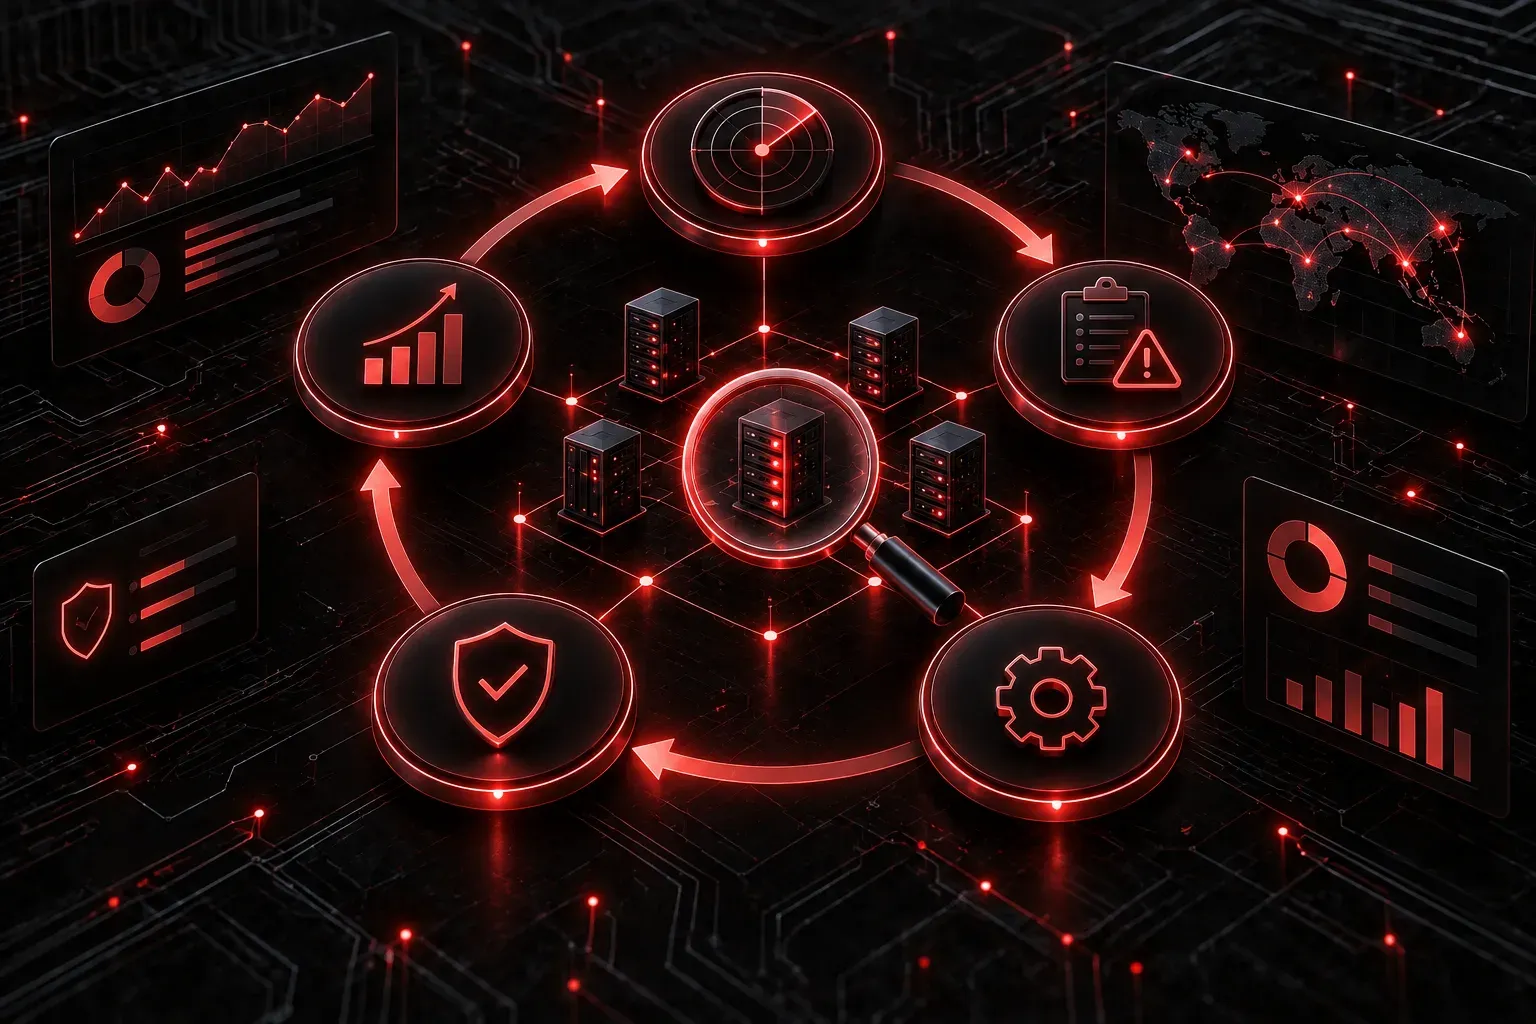
Before you can protect a system, you need to know what's wrong with it. That's the core idea behind vulnerability management: a structured, repeatable process for finding weaknesses in your environment and doing something about them before attackers do.
For the CCST Cybersecurity exam, you'll need to understand the vulnerability management process at a conceptual level. This guide breaks it down into clear, practical steps you can actually remember and apply.
What Is Vulnerability Management?
Vulnerability management is an ongoing cybersecurity process that involves identifying, evaluating, prioritizing, and remediating security weaknesses in systems, applications, and networks. It's not a one-time task; it's a lifecycle that repeats continuously as your environment changes and new vulnerabilities are discovered.
Think of it like maintaining a car. You don't just change the oil once and forget about it. You follow a regular schedule, check what needs attention, fix what's broken, and repeat.
The Vulnerability Management Lifecycle
The vulnerability lifecycle typically follows five core phases. Let's walk through each one.
1. Discovery (Identify What You Have)
You can't protect what you don't know exists. The first step is building an inventory of all assets in your environment: servers, workstations, network devices, cloud instances, and applications. This is sometimes called asset discovery.
Once you know what's in your environment, vulnerability scanners like Nessus, OpenVAS, or Qualys can probe those assets to find known weaknesses. These tools compare system configurations and software versions against databases of known vulnerabilities, including the CVE (Common Vulnerabilities and Exposures) list.
2. Prioritization (What Matters Most?)
A typical scan might return hundreds or even thousands of findings. You can't fix everything at once, so prioritization is critical. This is where risk management thinking comes in.
Vulnerabilities are typically scored using the CVSS (Common Vulnerability Scoring System), which rates severity on a scale from 0 to 10. A score of 9.8 is critical; a score of 2.1 is low. But the score alone doesn't tell the whole story. You also need to consider:
- Exploitability: Is there a known exploit actively being used in the wild?
- Asset value: Does this vulnerability affect a critical server or a rarely-used test machine?
- Exposure: Is the vulnerable system internet-facing or isolated internally?
3. Remediation (Fix It)
Remediation means actually addressing the vulnerability. The most common method is applying a patch, which is an update released by the software vendor to fix the flaw. Other options include:
- Configuration changes: Disabling an unnecessary service or closing an open port
- Compensating controls: Adding a firewall rule or IDS signature when a patch isn't available yet
- Removal: Uninstalling software that is no longer needed or supported
4. Verification (Did It Work?)
After remediation, you need to confirm the fix actually worked. This means running another scan against the affected system to verify the vulnerability no longer appears. Skipping this step is a common mistake; patches sometimes fail to apply correctly or only partially resolve an issue.
5. Reporting and Monitoring (Track Progress Over Time)
Vulnerability management isn't just a technical exercise; it's also a communication process. Security teams need to report findings to management, track remediation progress, and demonstrate that risk is being reduced over time. Regular reporting helps organizations understand their overall security posture and make informed decisions about where to invest resources.
Monitoring also ensures that newly discovered vulnerabilities are caught in the next cycle, keeping the process continuous rather than reactive.
Why This Matters for Cybersecurity
Most successful cyberattacks exploit known vulnerabilities, not zero-days. That means a consistent vulnerability management process is one of the most effective defenses available. It reduces your attack surface, demonstrates due diligence, and helps your organization stay ahead of threats rather than chasing them.
Understanding these cybersecurity steps gives you a foundation for thinking about security as a process, not just a product.
What's Next
Now that you understand how vulnerability management works, the next step is learning how vulnerabilities are actually classified and scored. In the next post, we'll dig into CVSS scores and CVE identifiers so you can read security advisories and make sense of what they're really telling you.