
Containment Strategies in Incident Response
This post breaks down incident containment strategies for Security+ learners, covering both short-term and long-term containment approaches. It explains how to limit damage during a security incident without destroying evidence, and how containment fits into the broader NIST incident response lifec

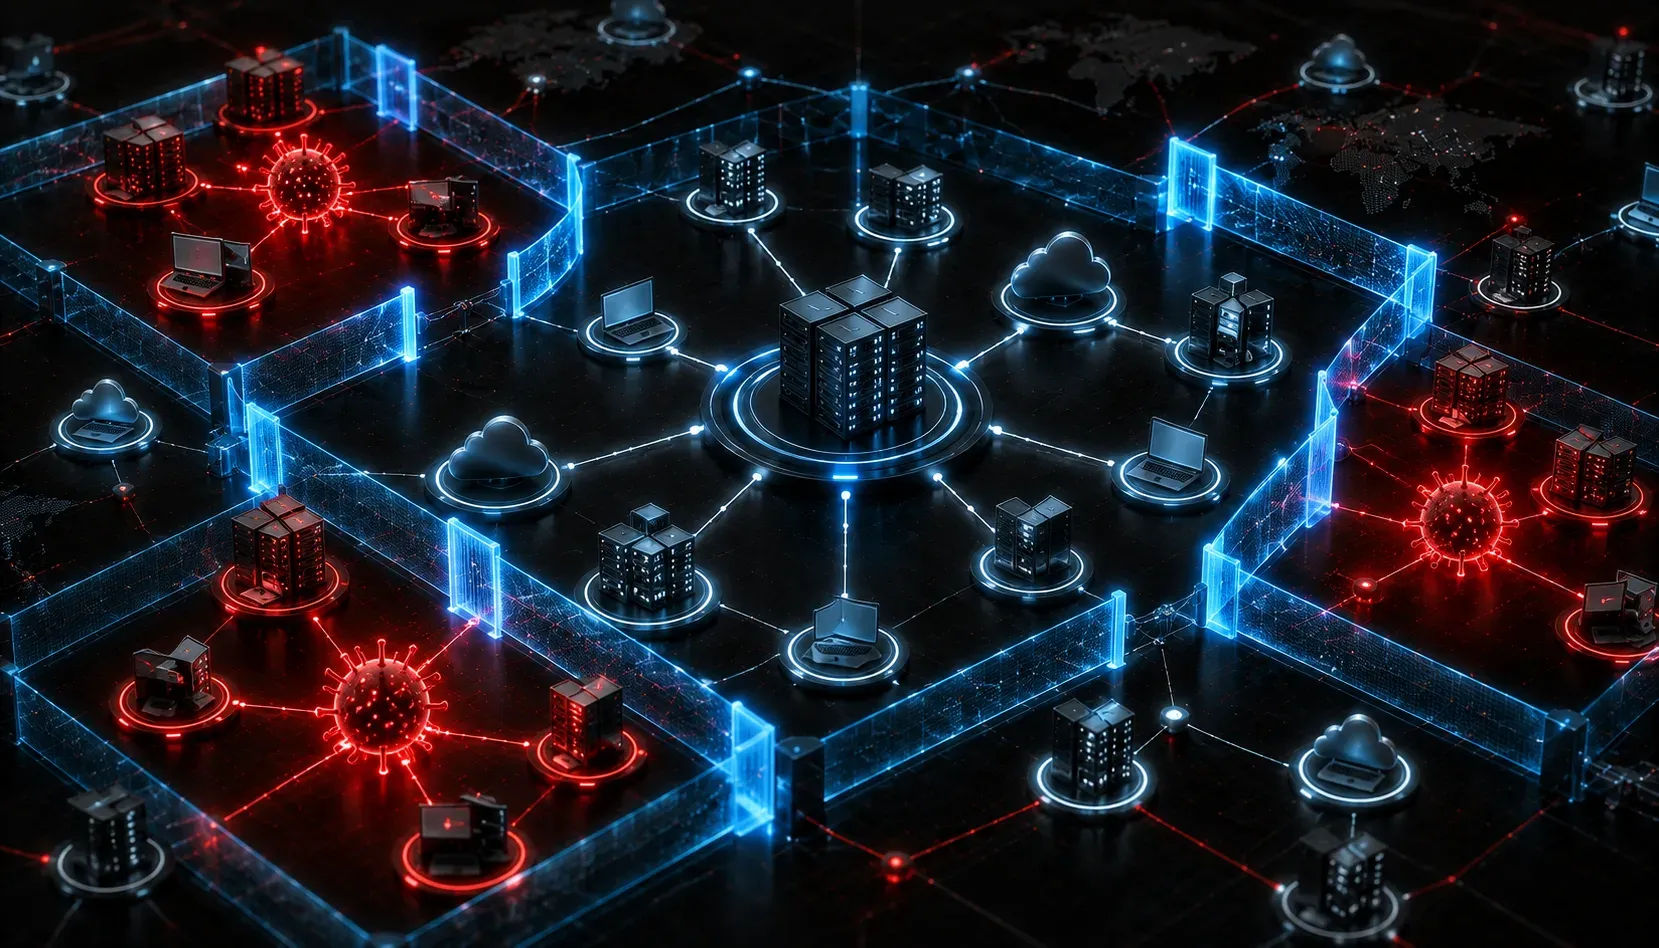
What Is Containment and Why Does It Matter?
When a security incident occurs, your first instinct might be to immediately wipe the affected system and start fresh. That approach, while understandable, can destroy valuable evidence and actually make things worse. Containment is the phase where you stop the bleeding without losing the patient.
In incident response, containment means taking deliberate steps to limit the spread and impact of an incident while preserving your ability to investigate and recover. Think of it like a doctor stabilizing a trauma patient before surgery. You're not fixing everything right now; you're making sure things don't get worse while you prepare a proper response.
For the CompTIA Security+ exam (Objective 4.8), understanding containment strategies is essential. Let's break down how this works in practice.
The Two Phases of Containment
Short-Term Containment
Short-term containment focuses on immediate damage control. The goal is to stop the threat from spreading right now, even if the solution is temporary. Common short-term actions include:
- Isolating the affected system: Disconnecting a compromised host from the network prevents lateral movement to other systems.
- Disabling a compromised account: If credentials have been stolen or abused, locking the account cuts off the attacker's access path.
- Blocking a malicious IP address: Adding a firewall rule to drop traffic from a known bad actor is a fast and effective first step.
- Segmenting network traffic: Using VLANs or access control lists to wall off a suspicious segment of the network limits the blast radius of the incident.
Short-term containment is about buying time. You're not done when these steps are complete; you've just created breathing room for the next phase.
Long-Term Containment
Long-term containment involves more durable security containment measures that allow the organization to keep operating while a full investigation and remediation plan is developed. Examples include:
- Patching vulnerable systems: Applying the fix that closes the attack vector the adversary used.
- Rebuilding compromised hosts: Sometimes a clean rebuild from a known-good image is the safest path forward.
- Resetting credentials organization-wide: If there's any chance of credential compromise at scale, a broader password reset reduces ongoing risk.
- Deploying enhanced monitoring: Increasing logging verbosity or deploying additional detection tooling gives you better visibility while the investigation continues.
Key Containment Decisions You'll Face
Not every incident calls for the same response measures. Before taking action, experienced responders ask a few critical questions:
- Will containment actions alert the attacker and cause them to escalate or destroy evidence?
- What is the business impact of taking a system offline?
- Do we need to preserve forensic evidence before making any changes?
- Is this a targeted attack or broad malware spreading across the environment?
For example, in a ransomware incident, isolating infected systems immediately is almost always the right call. But in an advanced persistent threat scenario, law enforcement or leadership may want you to monitor the attacker's behavior before tipping them off. Context drives the decision.
Containment in the Broader Incident Response Lifecycle
Containment sits between the Detection and Analysis phase and the Eradication and Recovery phase in the NIST incident response framework. It is not the finish line; it is the checkpoint. Once you have contained the threat, your team can move confidently into eradication (removing the root cause) and recovery (restoring normal operations).
Documentation during containment is critical. Every action taken, every system touched, and every decision made should be logged with timestamps. This record supports both forensic investigation and any legal or compliance obligations that follow.
What's Next
Now that you understand how to limit damage through containment, the next logical step is learning about eradication and recovery: how to fully remove the threat from your environment and safely restore systems to normal operation. We'll cover that in the next post in this series, including how to validate that an attacker is truly gone before bringing systems back online.
If you want to go deeper on incident response concepts for your Security+ exam, pick up the CompTIA Security+ Study Guide by Mike Chapple and David Seidl. It covers this entire domain with practice questions that match the exam format closely.