
Understanding the Steps in the Risk Management Process
This post walks beginners through the core steps of the risk management process, including how to identify risks, conduct a risk assessment, choose a response strategy, and implement solutions. It connects each step to real-world security practice and CompTIA Security+ exam objective 5.2. Practical

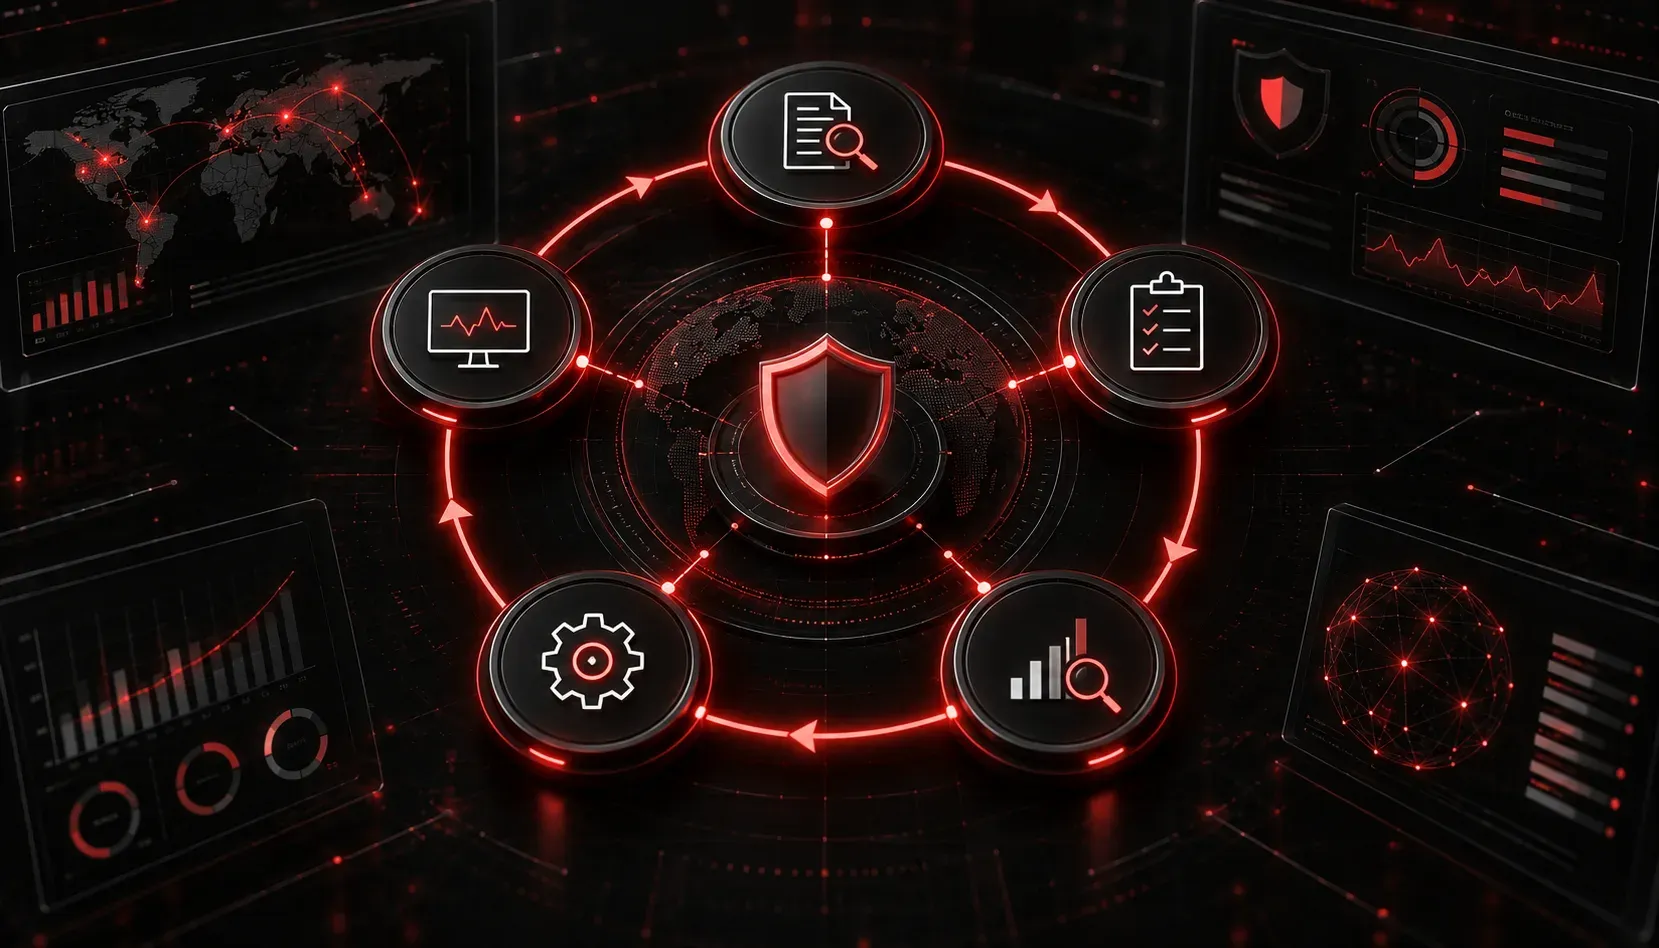
Risk management is one of those topics that sounds intimidating at first, but once you break it down into steps, it becomes much more approachable. For the Security+ exam and in real-world security work, understanding how organizations manage risk is essential. Let's walk through each step so you can confidently apply this knowledge on the exam and in practice.
What Is Risk Management?
Risk management is the ongoing process of identifying, assessing, and responding to potential threats that could harm an organization's assets, operations, or reputation. The goal is not to eliminate all risk (that's impossible) but to reduce it to an acceptable level. Every organization has limited resources, so risk management helps prioritize where to focus security efforts.
The Core Risk Management Steps
Step 1: Identify Risks
The first step is to identify risks that could affect the organization. This means cataloging potential threats and vulnerabilities across people, processes, technology, and physical assets. Common sources to consider include:
- Internal threats: Disgruntled employees, misconfigured systems, weak access controls
- External threats: Hackers, ransomware groups, nation-state actors
- Environmental threats: Natural disasters, power outages, hardware failures
The output of this step is a risk register, which is a documented list of all identified risks. Think of it as your master inventory of "things that could go wrong."
Step 2: Assess the Risks
Once risks are identified, you need to analyze them during the risk assessment phase. This involves evaluating two key factors:
- Likelihood: How probable is it that this risk will actually occur?
- Impact: If it does occur, how severe would the consequences be?
Risk assessment can be done qualitatively (using labels like low, medium, or high) or quantitatively (using actual dollar figures). For example, a quantitative approach might calculate the Annual Loss Expectancy (ALE) using this formula:
ALE = Single Loss Expectancy (SLE) x Annualized Rate of Occurrence (ARO)If a server worth $50,000 has a 20% chance of being compromised each year, the ALE would be $10,000. This helps leadership make informed, data-driven decisions about security spending.
Step 3: Analyze Risk Response Options
After assessment, you choose how to respond to each risk. There are four standard risk response strategies:
- Avoid: Stop the activity that creates the risk altogether
- Mitigate: Reduce the likelihood or impact through security controls
- Transfer: Shift the financial risk to a third party (such as purchasing cyber insurance)
- Accept: Acknowledge the risk and choose to do nothing, typically when the cost of mitigation exceeds the potential impact
Choosing the right response requires balancing security needs with business goals and budget constraints.
Step 4: Implement Solutions
This is where decisions become actions. Based on the chosen response strategy, the organization implements solutions such as deploying firewalls, enforcing multi-factor authentication, patching vulnerable systems, or updating security policies. Implementation should include clear ownership, timelines, and documentation so accountability is maintained.
Step 5: Monitor and Review
Risk management is not a one-time project. After implementing solutions, you continuously monitor their effectiveness and watch for new risks that may emerge. This could involve reviewing security logs, running vulnerability scans, or conducting periodic audits. If the threat landscape changes, the process loops back to Step 1.
Why This Matters for Security+
Exam objective 5.2 tests your ability to explain elements of the risk management process. You should be able to define each step, distinguish between qualitative and quantitative risk assessment, and understand the four risk response strategies. Expect scenario-based questions asking you to identify which strategy applies to a given situation.
What's Next
Now that you understand the risk management steps, the next concept to explore is how organizations quantify risk using specific metrics like SLE, ARO, and ALE in more detail. Understanding the math behind quantitative risk analysis will give you a significant advantage on exam day.