
Building a Comprehensive AI Governance Strategy
This post walks IT professionals through the four core pillars of an AI governance strategy: policy frameworks, risk management, regulatory compliance, and governance integration. It provides practical, actionable guidance for building a comprehensive plan that can be adapted to any organization's
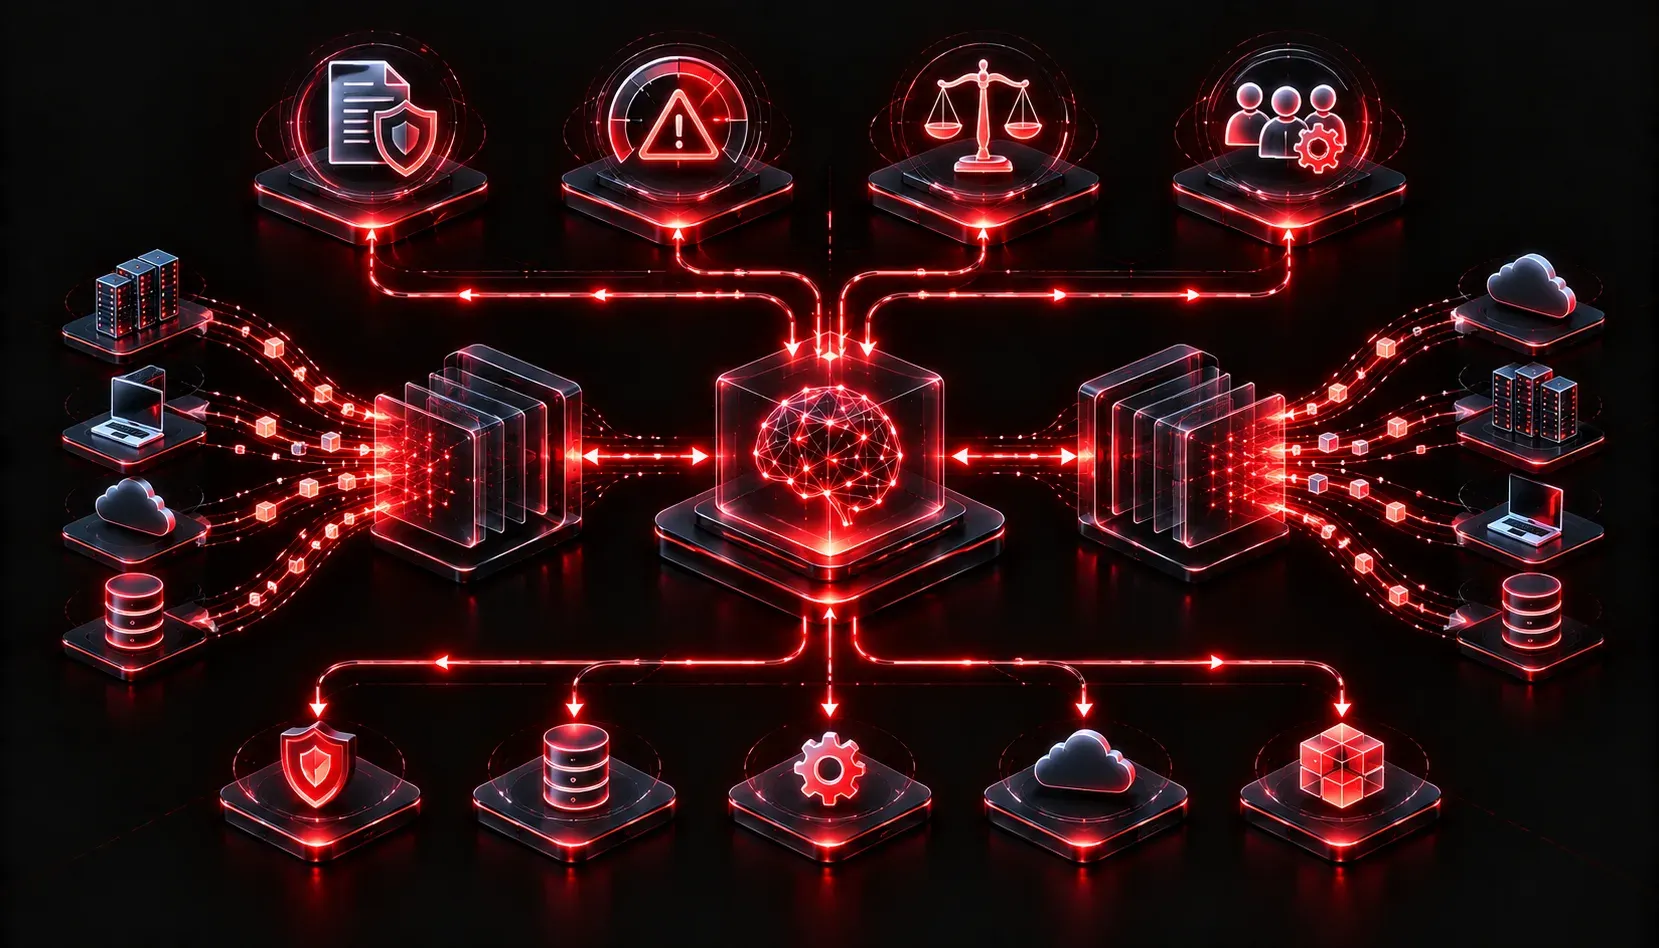
Deploying AI in an organization without a governance strategy is like running a network without access control lists: things might work for a while, but you are one misconfiguration away from a serious problem. A well-built AI governance strategy gives you the structure to deploy AI responsibly, manage risk, and stay on the right side of evolving regulations.
This post walks you through the core components of a comprehensive plan for AI governance integration. Think of it as a blueprint you can adapt to your organization's size, industry, and risk appetite.
Why Governance Comes Before Deployment
It is tempting to grab the latest AI tool, plug it into your workflows, and figure out the rules later. Resist that urge. The organizations that face the biggest compliance and reputational problems are the ones that treated governance as an afterthought. A proactive AI governance strategy does three things:
- Reduces legal and regulatory exposure: Frameworks like the EU AI Act, NIST AI RMF, and emerging US state laws impose real obligations. Knowing which ones apply to you before deployment keeps you compliant.
- Builds stakeholder trust: Employees, customers, and regulators want to know someone is accountable for AI decisions.
- Creates repeatable processes: Ad hoc AI adoption creates chaos. Governance turns one-off decisions into documented, auditable workflows.
The Four Pillars of a Comprehensive AI Governance Plan
1. Policy Framework
Your policy layer defines the rules of the road. A solid AI policy framework should answer these questions:
- What AI tools and systems are approved for use?
- Who is authorized to deploy or modify AI systems?
- What data can be fed into AI systems, and what is explicitly off-limits?
- How are AI-generated outputs reviewed before acting on them?
Start with an Acceptable Use Policy (AUP) for AI, then layer in data handling guidelines, vendor assessment criteria, and documentation requirements. Your policies should be written in plain language, reviewed by legal, and communicated to all staff who interact with AI tools, not just the technical team.
2. Risk Management
The NIST AI Risk Management Framework (AI RMF) is one of the most practical references available. It organizes AI risk management into four functions:
- Govern: Establish accountability structures, roles, and organizational culture around responsible AI.
- Map: Identify and categorize AI risks in context, including bias, safety, privacy, and security.
- Measure: Quantify and evaluate risks using appropriate metrics and testing methods.
- Manage: Prioritize and treat risks through controls, mitigations, and monitoring.
For each AI system you operate, document a risk profile. Include the intended use case, data inputs, output types, potential failure modes, and who is accountable if something goes wrong. This does not need to be a 100-page document. A well-structured one-pager per system is often enough to start.
3. Regulatory Compliance
Compliance requirements vary by industry, geography, and AI use case. A healthcare organization using AI for patient triage faces different obligations than a retailer using AI for inventory forecasting. At a minimum, map your AI systems against:
- GDPR or CCPA: If your AI processes personal data, privacy regulations apply.
- EU AI Act risk tiers: High-risk AI applications (biometrics, critical infrastructure, employment decisions) face strict requirements.
- Industry-specific rules: HIPAA for healthcare, FFIEC guidance for financial services, and similar sector-specific frameworks.
Create a simple compliance matrix that maps each AI system to the regulations that apply, then assign an owner responsible for tracking changes in those regulations.
4. Governance Integration
A governance strategy only works if it is embedded in actual workflows, not sitting in a shared drive nobody reads. Governance integration means:
- Adding an AI risk review step to your existing project intake or change management process.
- Including AI considerations in vendor due diligence questionnaires.
- Establishing a cross-functional AI Review Board or committee with representation from IT, legal, compliance, and business units.
- Scheduling regular audits of AI systems in production, not just at initial deployment.
The goal is to make responsible AI decision-making a natural part of how work gets done, rather than a separate compliance exercise that everyone ignores.
A Practical Starting Point
If your organization has no formal AI governance today, start small. Conduct an AI inventory: document every AI tool currently in use, even the unofficial ones. From that inventory, identify your highest-risk use cases and build your first policy and risk profile around those. Governance integration does not require a perfect system on day one. It requires a starting point and a commitment to iterate.
What's Next
With your governance strategy framework in place, the next natural step is understanding how to evaluate specific AI vendors and tools against your governance criteria. Upcoming posts in this series cover AI vendor risk assessments and how to apply governance thinking to real-world AI implementation decisions.