
How Authentication and Authorization Work
Authentication and authorization are two distinct but connected processes that work together to secure network access. Authentication verifies identity, while authorization determines what an authenticated user is permitted to do. Understanding both is essential for the CCST Cybersecurity exam and

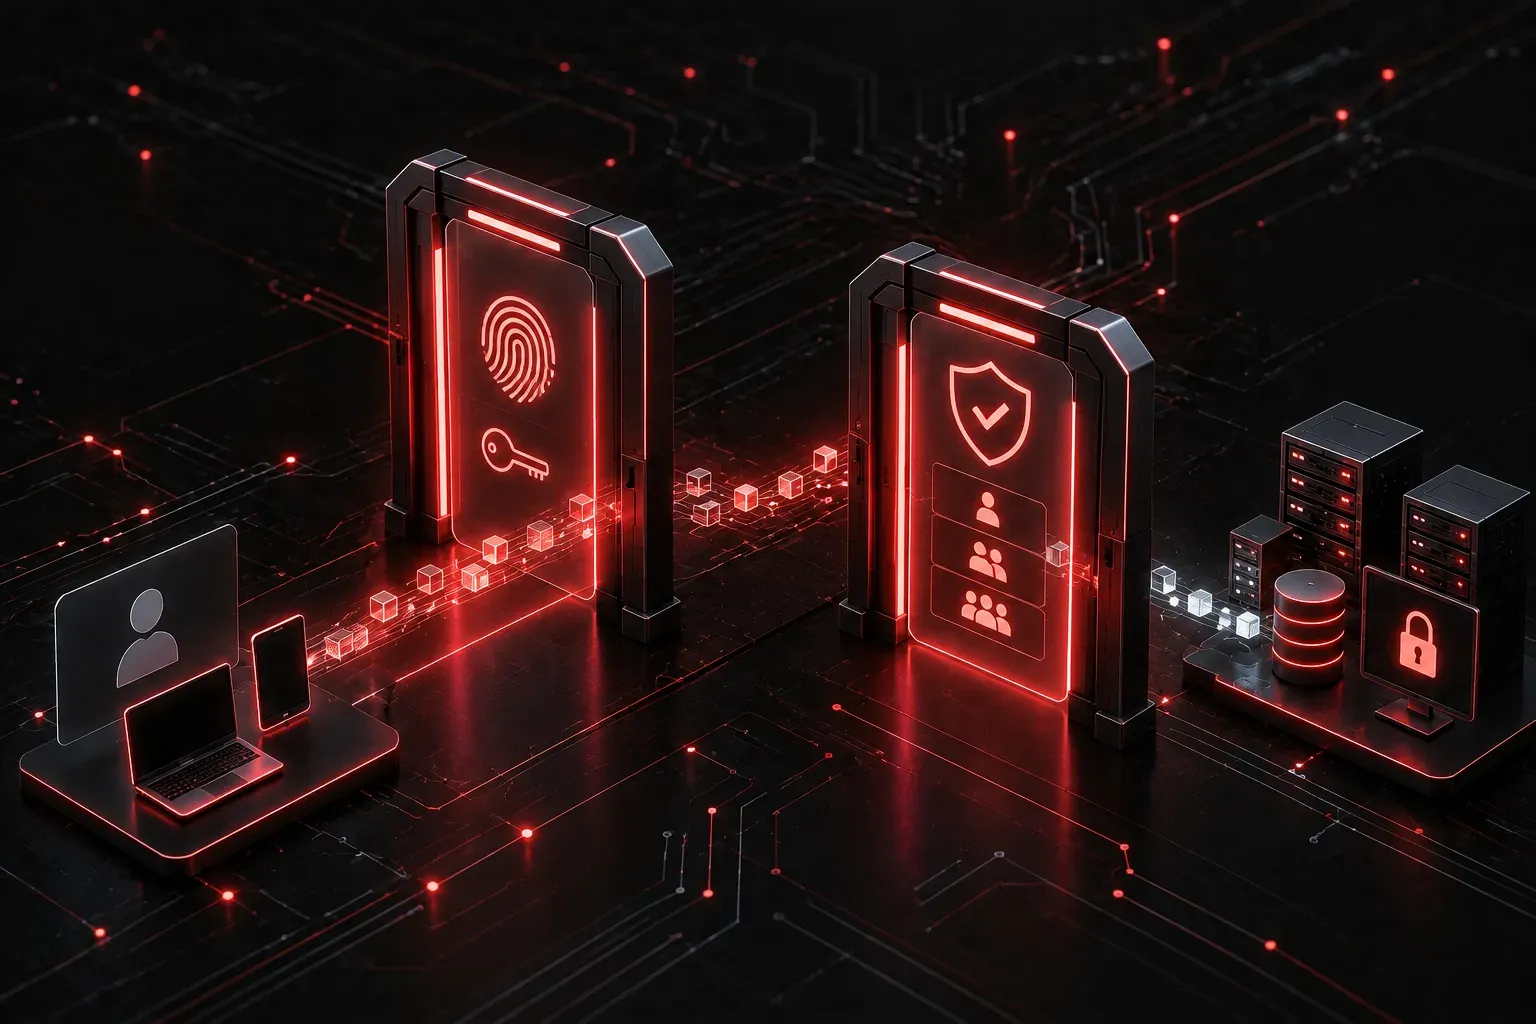
When you log into a website, swipe a badge at a door, or connect to a corporate VPN, two separate security processes are happening behind the scenes. These processes are called authentication and authorization, and understanding the difference between them is one of the most foundational concepts in cybersecurity. They work together to provide secure access and network protection, but they each do something very different.
Authentication: Proving Who You Are
Authentication is the process of verifying your identity. It answers the question: Are you who you claim to be? Before any system grants access, it needs to confirm that you are a legitimate user.
Identity verification typically relies on one or more of three factors:
- Something you know: a password, PIN, or security question answer
- Something you have: a smart card, hardware token, or mobile device
- Something you are: a fingerprint, facial recognition, or retina scan (biometrics)
Using more than one of these factors together is called multi-factor authentication (MFA). For example, entering a password and then entering a code sent to your phone is MFA. This approach is far more secure than a password alone because compromising one factor is not enough for an attacker to gain access.
A practical example: when you enter your username and password into a login page, the system checks those credentials against a stored database. If they match, authentication succeeds. If they do not match, access is denied at this step before anything else even happens.
Authorization: Determining What You Can Do
Once a system has confirmed your identity, authorization takes over. Authorization answers the question: What are you allowed to do? Just because someone is authenticated does not mean they can access everything on a network or system.
Think of it this way: a hospital employee might authenticate successfully with their badge and PIN. However, a nurse has different access rights than a billing administrator. The nurse can view patient records; the billing admin can view financial data. Neither can access the other's resources. That controlled access is authorization in action.
Authorization is commonly implemented through:
- Role-Based Access Control (RBAC): permissions are assigned based on a user's role within an organization
- Access Control Lists (ACLs): rules that specify which users or systems can access specific resources
- Least Privilege: users are granted only the minimum permissions needed to do their job
Why the Distinction Matters
Mixing up these two concepts is a common mistake, but they are distinct steps in a security process. Authentication always comes first. Authorization cannot happen without a confirmed identity to evaluate.
Consider this simplified flow:
User submits credentials
        |
        v
[Authentication] --> Credentials valid? --> NO --> Access Denied
        |
       YES
        |
        v
[Authorization] --> Permission granted? --> NO --> Access Denied
        |
       YES
        |
        v
   Access Granted to allowed resources
A security gap in either step creates risk. If authentication is weak, attackers can impersonate legitimate users. If authorization is misconfigured, even authenticated users might access sensitive data they should never see. Both layers must be properly implemented for real network protection.
A Real-World Cisco Context
On Cisco devices, authentication and authorization are commonly managed using AAA, which stands for Authentication, Authorization, and Accounting. A TACACS+ or RADIUS server handles these functions centrally, so every device on the network enforces access control consistently. Even at the CCST level, understanding that AAA exists and why it matters gives you a strong foundation for more advanced security topics.
What's Next
Now that you understand authentication and authorization as separate but connected processes, the next step is looking at the tools and protocols that make them work in practice. Upcoming posts in this series will cover topics like AAA frameworks, password security best practices, and how firewalls and access control lists enforce network protection at the device level. Each piece builds on this foundation, so you are in a great place to keep going.