
Managing Networks in a Remote Work Era
Remote work fundamentally changed how networks are designed and managed. This post explores the key adaptations including VPNs, Zero Trust, SD-WAN, and cloud services that organizations deployed to support distributed workforces, and why these concepts matter for Network+ Exam Objective 1.8.
Remote work transformed from a rare perk into a fundamental business requirement almost overnight. For network professionals, this shift created a new set of challenges that traditional campus-focused network design simply was not built to handle. Understanding how networks have adapted to support remote workers is increasingly important, and it is directly relevant to your Network+ studies.
The Traditional Network Model and Its Limitations
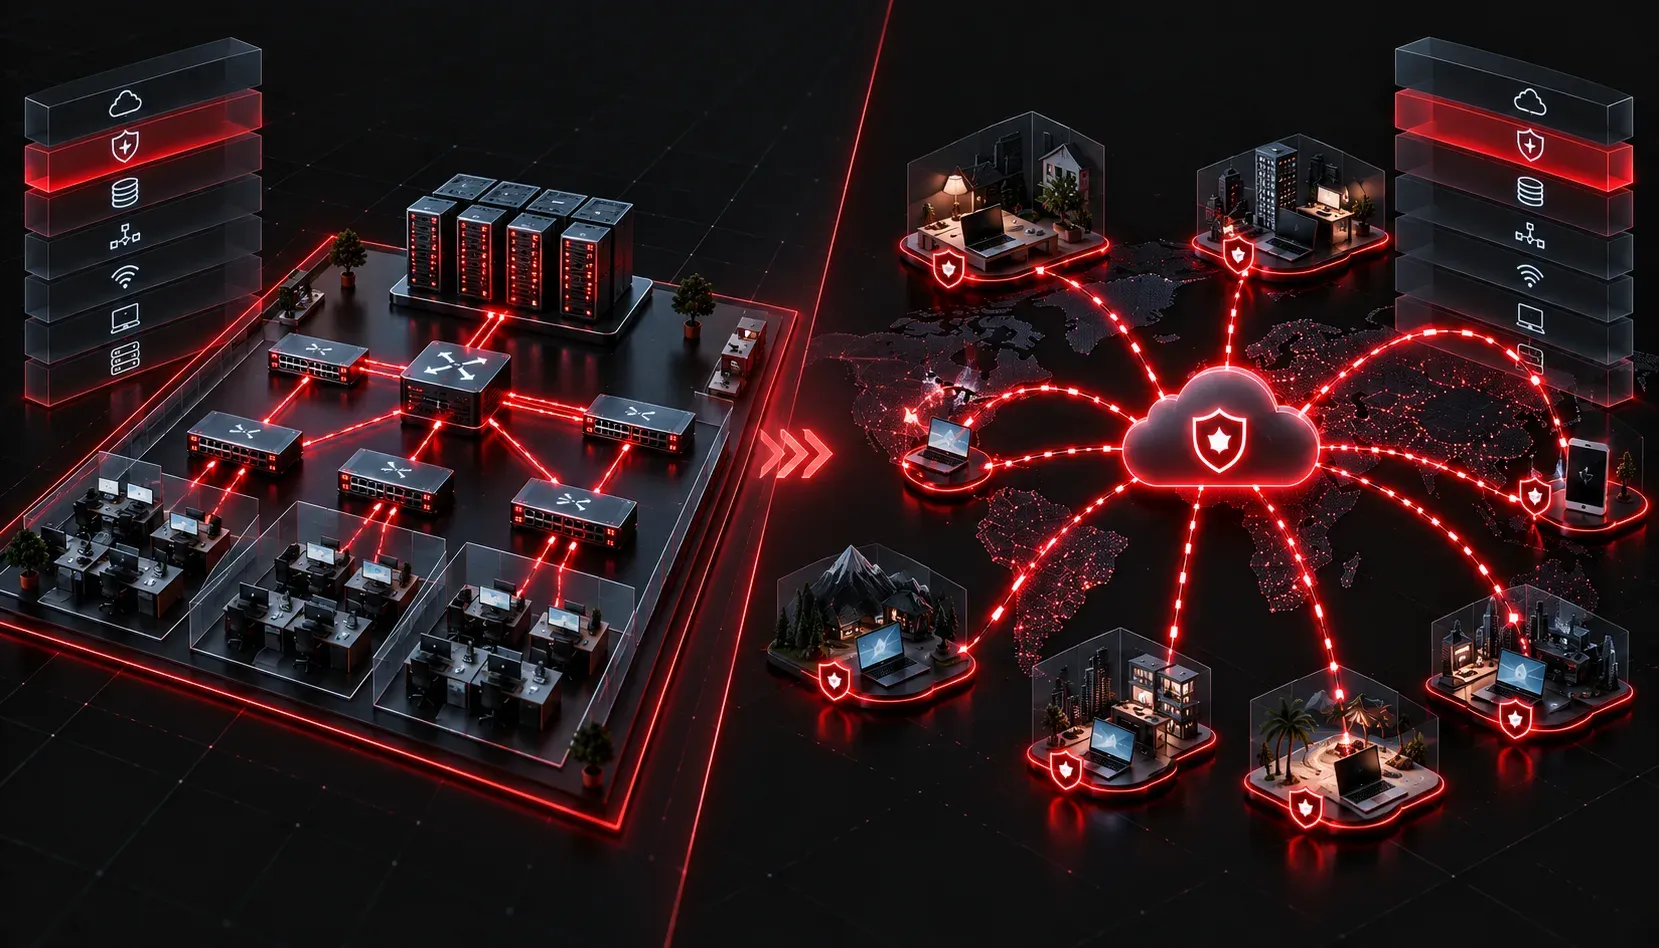
Before the remote work era, most corporate networks followed a hub-and-spoke design. Users sat inside a physical building, connected to switches, which fed into routers, which eventually reached the internet or a data center. Security controls lived at the perimeter. Traffic patterns were predictable. Bandwidth was sized for on-site use.
When work from home became widespread, that model cracked. Suddenly, thousands of endpoints sat outside the perimeter. Users accessed corporate resources over residential ISPs, shared home networks with streaming devices and gaming consoles, and connected from locations with no IT oversight whatsoever. Network management could no longer assume physical presence or a controlled environment.
Key Remote Adaptations in Network Design
VPNs as a First Line of Defense
The most immediate adaptation was the widespread deployment of Virtual Private Networks. A VPN creates an encrypted tunnel between a remote device and the corporate network, making it appear as though the user is physically on-site. This protects data in transit over untrusted networks like home Wi-Fi or coffee shop hotspots.
Two VPN architectures became critical talking points for remote work networks:
- Full Tunnel VPN: all traffic from the remote device routes through the corporate network, giving IT maximum visibility and control.
- Split Tunnel VPN: only corporate-bound traffic goes through the VPN, while general internet traffic exits locally. This reduces strain on corporate infrastructure but limits visibility.
Choosing between these two involves a trade-off between security oversight and bandwidth efficiency, something network teams had to decide quickly during the shift to remote work.
Zero Trust Network Access
Traditional security operated on a simple assumption: if you are inside the network, you are trusted. Remote work networks exposed how dangerous that assumption was. Zero Trust flips the model entirely. Every user, device, and connection must be authenticated and verified, regardless of location.
In a Zero Trust model, access is granted based on identity, device health, and context rather than network location. This makes it far more resilient for a distributed workforce where the "inside" of the network no longer has a clear boundary.
Cloud Services and SD-WAN
Remote adaptations also accelerated the move toward cloud-hosted services. When users are distributed globally, routing everyone through a central data center creates unnecessary latency. Many organizations shifted to SaaS (Software as a Service) tools like Microsoft 365 or Google Workspace, reducing the need for traffic to pass through corporate infrastructure at all.
SD-WAN (Software-Defined Wide Area Network) became another popular solution. It allows organizations to intelligently route traffic across multiple connection types, including broadband, LTE, and MPLS, based on real-time conditions. This is especially useful when remote sites or home workers need reliable, high-performance connectivity without expensive dedicated circuits.
Network Management Challenges in a Remote Era
Beyond the technology changes, day-to-day network management shifted considerably. IT teams now deal with:
- Endpoint diversity: personal devices, unmanaged home routers, and inconsistent operating system versions create a much harder-to-secure environment.
- Bandwidth unpredictability: residential internet connections vary wildly in speed and reliability, affecting VoIP, video conferencing, and real-time applications.
- Visibility gaps: traditional monitoring tools designed for on-premise networks often miss activity happening outside the corporate perimeter.
- Help desk complexity: troubleshooting a user's home network remotely requires different tools and skills than walking to a desk on-site.
Tools like SNMP, remote monitoring software, and cloud-based network management platforms became essential for maintaining visibility across a dispersed workforce.
What This Means for Your Network+ Studies
The Network+ exam, particularly Objective 1.8, expects you to understand how network services and infrastructure support real-world use cases. Remote work networks are a perfect example of concepts like VPNs, network security models, and WAN technologies applied in a practical context. Rather than memorizing definitions in isolation, think about how each technology solves a specific problem created by distributed users.
What's Next
Now that you understand how remote work has reshaped network design, the next step is going deeper on the technologies that make it all possible. Coming up, we will explore VPN types in detail, including how IPsec and SSL/TLS VPNs differ and when you would choose one over the other. Understanding the mechanics behind these tunnels will strengthen both your exam performance and your real-world troubleshooting skills.
Tools and resources for this topic
- CompTIA Network+ Study Guide — Comprehensive N10-009 exam preparation covering all five domains.