
SSH vs Telnet: Understanding the Differences
This post compares SSH and Telnet, explaining why Telnet's plain-text transmission makes it insecure and why SSH is the standard for secure remote access. It covers key differences including ports, encryption, and authentication, along with a practical SSH configuration example for Cisco IOS device

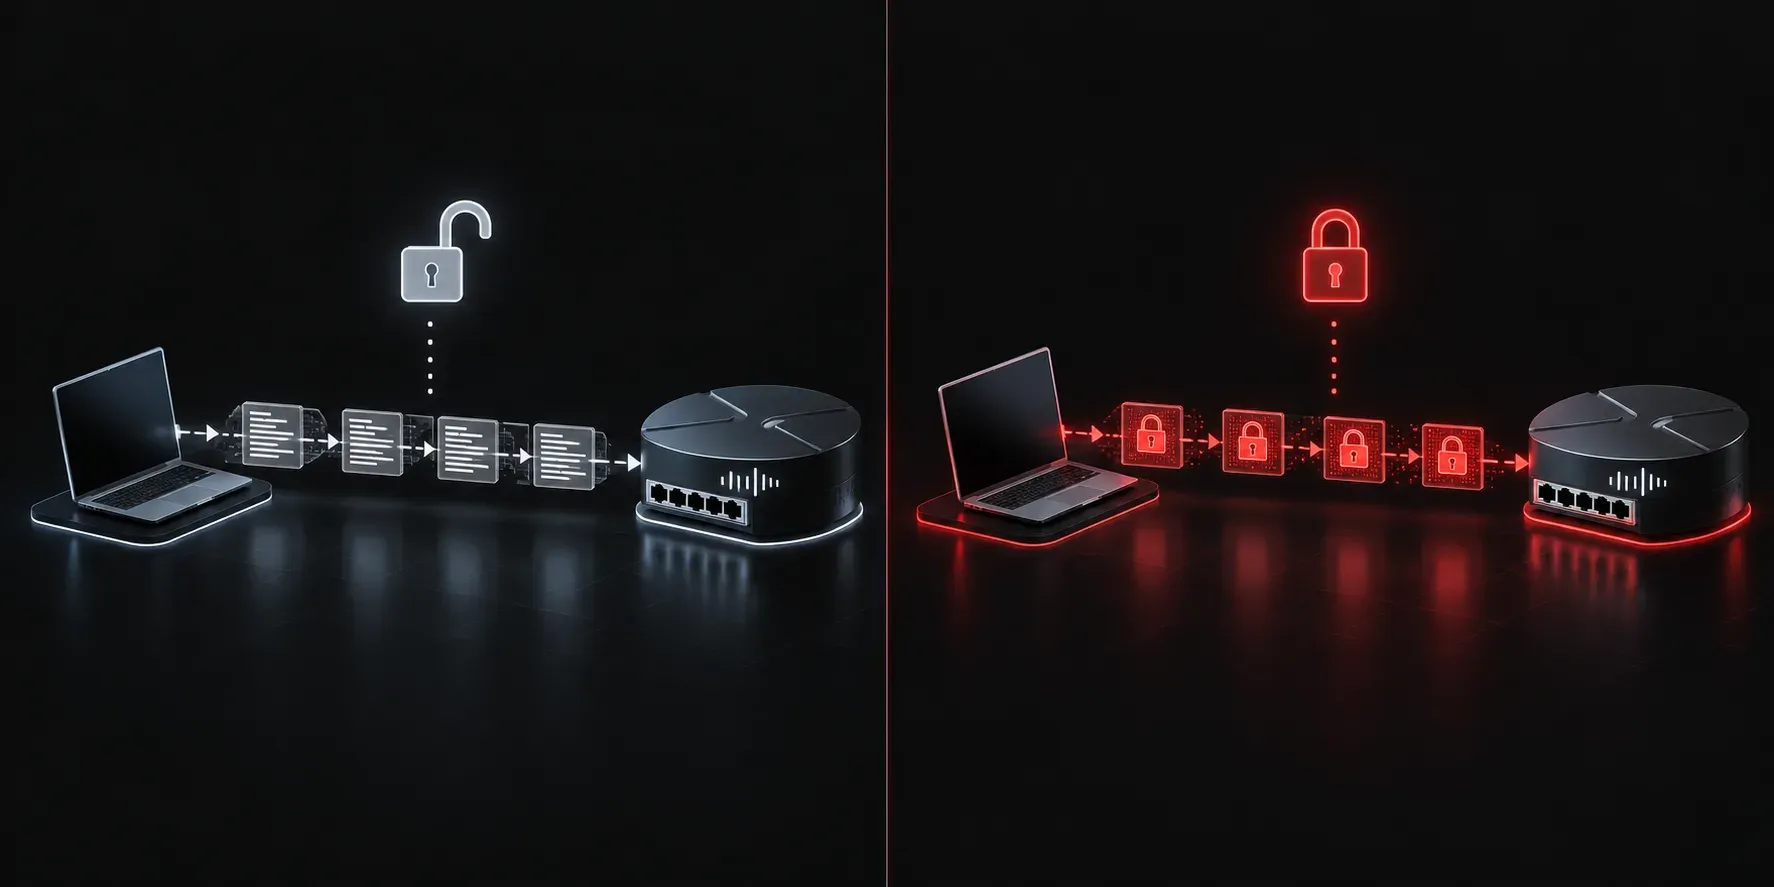
When you're managing network devices remotely, you need a way to access the command-line interface without being physically in front of the device. Two protocols have historically been used for this: Telnet and SSH. Understanding the SSH vs Telnet differences is not just exam knowledge, it's something every network engineer needs to understand before they touch a production device.
What is Telnet?
Telnet (Teletype Network) is one of the oldest remote access protocols, dating back to 1969. It operates on TCP port 23 and allows you to open a command-line session on a remote device over a network connection.
The critical problem with Telnet is simple: everything is sent in plain text. That means your username, your password, and every command you type travels across the network as readable characters. Anyone with a packet capture tool like Wireshark sitting between you and the device can read every single thing you type.
Here is what a Telnet login looks like in a packet capture. All of this is fully readable:
Username: admin
Password: cisco123
Router>enable
Password: enable123
That alone should tell you everything you need to know about why Telnet should never be used on a production network.
What is SSH?
SSH (Secure Shell) was designed specifically to solve the security problems with Telnet. It operates on TCP port 22 and uses encryption to protect everything transmitted during your session, including credentials and commands.
SSH uses public-key cryptography to authenticate the server and negotiate an encrypted session before any data is exchanged. Even if someone captures the packets, they see encrypted gibberish instead of readable text.
On a Cisco device, you can verify which version of SSH is running with:
Router# show ip ssh
SSH Enabled - version 2.0
Authentication timeout: 120 secs; Authentication retries: 3
You should always aim for SSHv2, which is more secure than version 1. SSHv1 has known vulnerabilities and should be avoided.
SSH vs Telnet: Side-by-Side Comparison
- Port: SSH uses
TCP 22; Telnet usesTCP 23 - Encryption: SSH encrypts all traffic; Telnet sends everything in plain text
- Authentication: SSH supports public-key and password authentication; Telnet uses password only, unencrypted
- Security: SSH is considered secure for remote access; Telnet is considered insecure and deprecated for production use
- Preferred version: Always use SSHv2 over SSHv1
Configuring SSH on a Cisco Device
Setting up SSH on a Cisco IOS device is straightforward. Here is the basic configuration you need:
Router(config)# hostname R1
R1(config)# ip domain-name anythingoverip.com
R1(config)# crypto key generate rsa modulus 2048
R1(config)# ip ssh version 2
R1(config)# line vty 0 4
R1(config-line)# transport input ssh
R1(config-line)# login local
R1(config)# username admin privilege 15 secret StrongPass123
A few things to note here. First, you must configure a hostname and ip domain-name before generating RSA keys, because Cisco uses both to create the key pair name. Second, setting transport input ssh on the VTY lines explicitly blocks Telnet connections, which is exactly what you want. Using transport input telnet ssh would allow both, which you should avoid.
Why This Matters for the CCNA Exam
Exam objective 4.8 specifically asks you to explain the function of SNMP in network operations, but SSH vs Telnet frequently appears across configuration and security scenarios in the CCNA 200-301 exam. You should be able to identify which ports each protocol uses, explain why SSH is preferred, and configure SSH on a Cisco router or switch from scratch.
What's Next
Now that you understand how to securely access a device remotely, the next logical step is understanding how network devices manage and report their own status. In the next post, we will look at SNMP (Simple Network Management Protocol), including how it works, the difference between versions, and how it fits into a network management strategy.
Tools and resources for this topic
- Wendell Odom CCNA Vol 1 — Covers networking fundamentals, switching, and routing basics.
- Wendell Odom CCNA Vol 2 — Covers advanced routing, WAN, infrastructure services, and security.