
Building AI Workflows to Mitigate Security Threats
This post walks IT professionals through building practical AI-powered security workflows to detect and respond to AI-specific threats like prompt injection, model poisoning, and AI-generated phishing. It covers threat mapping, tool integration, and a Python example for LLM-assisted email analysis.
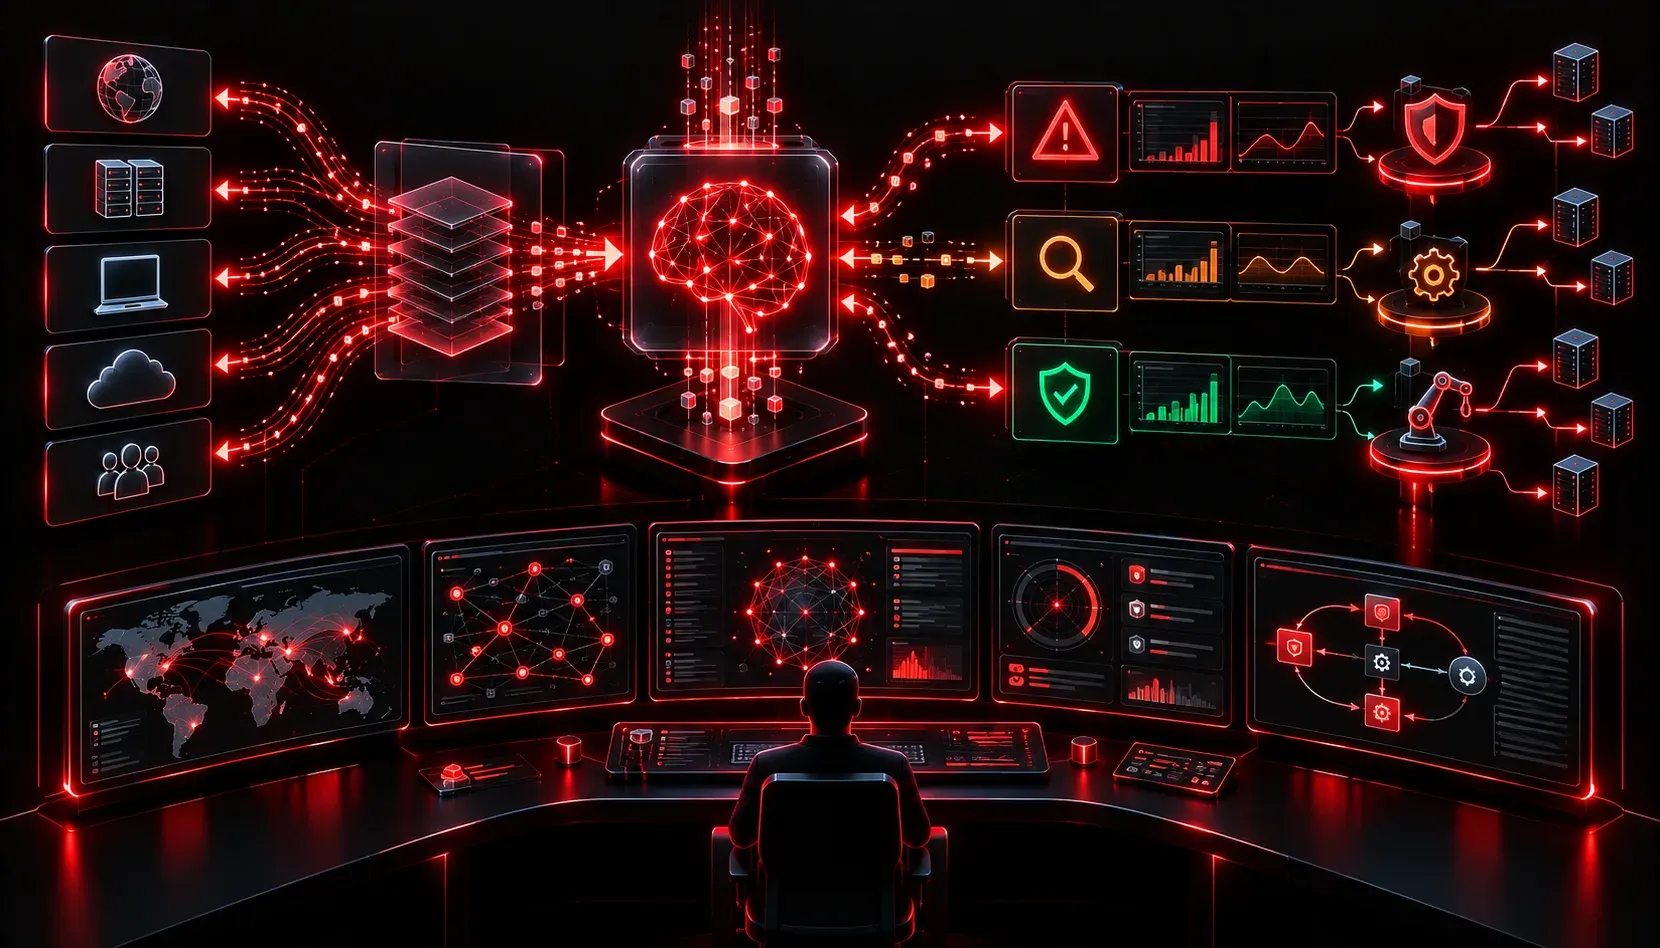
Security threats are not slowing down, and AI is changing the game on both sides of the fence. Attackers are using AI to craft more convincing phishing emails, generate malware variants faster than ever, and probe networks with automated precision. The good news is that you can fight back using the same technology. Building AI workflows for security gives you a structured, repeatable way to detect, analyze, and respond to threats at a speed no human team alone can match.
This post walks you through a practical approach to integrating AI tools into your security workflows, even if you are just getting started.
Understanding AI-Specific Threats First
Before you build a workflow, you need to know what you are defending against. AI introduces a unique category of threats that traditional security tools were not designed to handle:
- Prompt injection: Attackers manipulate AI systems by embedding malicious instructions inside user inputs, causing the model to behave in unintended ways.
- Model poisoning: Training data is tampered with to introduce biases or backdoors into AI models before deployment.
- Adversarial inputs: Carefully crafted inputs designed to fool AI classifiers, such as images that fool a computer vision system into misidentifying objects.
- AI-generated social engineering: Hyper-personalized phishing content generated by large language models (LLMs) at scale.
Knowing these threat types helps you design workflows that target the right detection points.
Step 1: Map Your Attack Surface
Start by identifying where AI touches your environment. Ask yourself: Are you running any AI-powered applications, chatbots, or APIs? Are your vendors using AI in their products? Where does user-supplied input enter an AI system?
Create a simple inventory. Even a spreadsheet works at this stage. For each AI touchpoint, note the input source, the model or service involved, and the output destination. This becomes the foundation of your threat model.
Step 2: Integrate AI Tools Into Your Detection Workflow
Once you know your attack surface, you can begin to integrate AI tools into your detection pipeline. Here are three practical entry points:
Log Analysis with AI Assistance
Tools like Elastic Security and Splunk now include built-in AI features for anomaly detection. Feed your security logs into these platforms and configure AI-assisted alerting rules. Instead of manually reviewing thousands of log lines, you get surfaced anomalies with context already attached.
Phishing Detection Using LLMs
You can use a simple API call to an LLM to pre-screen suspicious emails before they reach your analysts. Here is a basic Python example using the OpenAI API:
import openai

def analyze_email(email_body):
    client = openai.OpenAI()
    response = client.chat.completions.create(
        model="gpt-4o-mini",
        messages=[
            {
                "role": "system",
                "content": (
                    "You are a cybersecurity analyst. "
                    "Analyze the following email and determine if it "
                    "is a phishing attempt. Explain your reasoning."
                )
            },
            {
                "role": "user",
                "content": email_body
            }
        ]
    )
    return response.choices[0].message.content

sample_email = """
Dear User, your account has been suspended.
Click here immediately to verify: http://totally-legit-bank.ru/login
"""

print(analyze_email(sample_email))
This kind of lightweight screening can help triage high volumes of reported emails and flag the most suspicious ones for human review. Substitute the model identifier with whichever model your OpenAI account has access to; check OpenAI's model documentation for the current list of supported identifiers.
Prompt Injection Monitoring
If you run any internal LLM-based tools, add an input validation layer. Before passing user input to the model, run it through a sanitization check that looks for common injection patterns like embedded instructions or role-override attempts. Libraries like Rebuff are purpose-built for this.
Step 3: Close the Loop with AI-Assisted Response
Detection without response is just observation. Once a threat is flagged, your workflow should trigger a defined response. Use AI to help generate incident summaries, suggest remediation steps, or draft communications to stakeholders. Tools like Microsoft Sentinel include AI-powered playbooks that can automate containment actions based on alert type.
The goal is to reduce mean time to respond (MTTR) by having AI handle the repetitive triage and documentation tasks while your team focuses on decisions that require human judgment.
Keep Humans in the Loop
As you build these workflows, resist the temptation to fully automate everything. AI tools can produce false positives and miss novel threats. Every automated action should have a human review checkpoint, especially for high-impact responses like account lockouts or firewall rule changes. The best AI cybersecurity strategies treat AI as a force multiplier, not a replacement for skilled analysts.
What's Next
Now that you have a framework for building AI security workflows, the next step is understanding how to evaluate the trustworthiness of the AI tools you are bringing into your environment. In the next post, we will look at how to assess AI model transparency, bias, and vendor accountability as part of your broader security posture. That directly supports the ethics and governance principles covered in this domain.