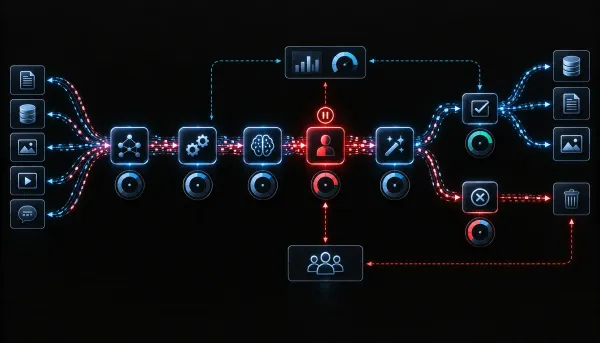
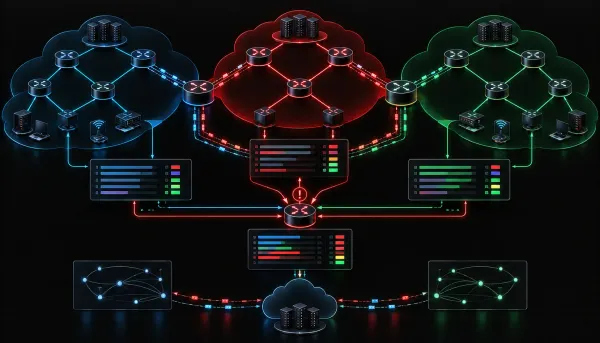
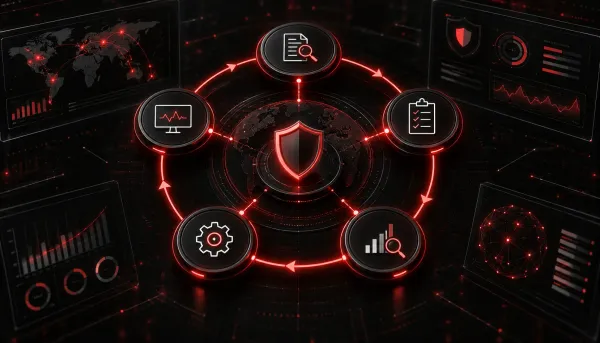
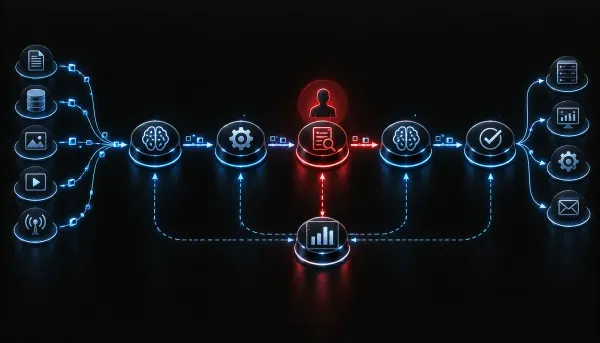
This post walks through a practical, step-by-step guide on how to conduct a third-party risk assessment, covering vendor inventory, risk tiering, security questionnaires, evidence review, and continuous monitoring. It aligns with Security+ Objective 5.3 and provides real-world context for supply ch